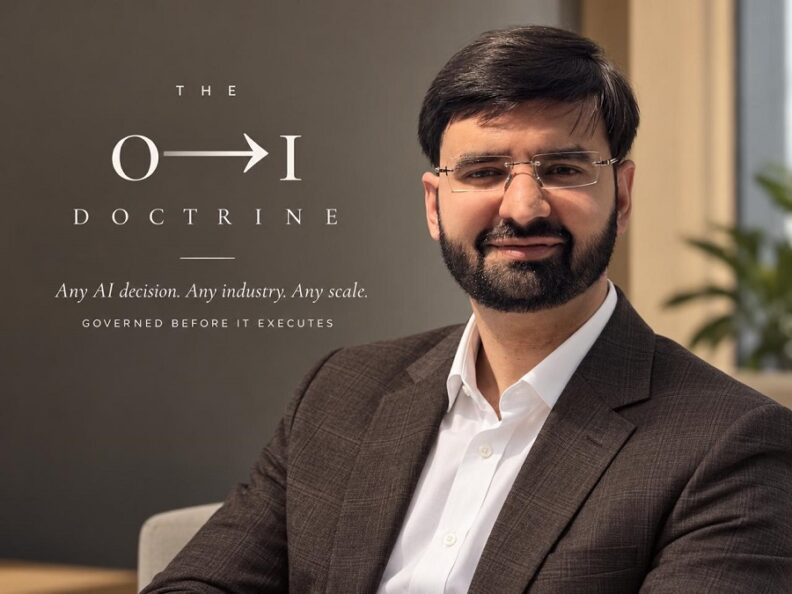
As the Superintelligence and AGI debate intensifies this week, inventor Vatsal Soin has filed a new patent on 23 September 2026 extending his 0 1 Doctrine — → the governance framework already covering AI decisions, biometrics, and financial transactions — into the zettabytes of dormant, dark data sitting unused inside the world’s clouds, financial systems, and archives.
Live: www.0to1doctrine.com
A GROWING FAMILY, ONE PARENT DOCTRINE
Each new filing is a child invention. The 0→1 Doctrine remains the parent.
The Doctrine proposes one governing idea across Soin’s patent portfolio: intelligence’s capability and its authority to act are separate things, each proposed action tested against an authorized boundary before execution, not explained after. His newest filing does not compete with the earlier ones — it is an organic extension of the same family, carrying that governing logic into zettabytes of stored data organizations pay to keep, proposing to convert standing cost into monetization income, real savings, and a lighter footprint.
THE PROBLEM: GIGAWATTS SPENT GUARDING NOTHING
Data centers burn power to protect records nobody has opened in a decade.
Industry estimates place global dark data — stored but never analyzed, never reused
— in the zettabytes, consuming gigawatts of continuous power simply to keep it encrypted, replicated, and backed up. None of it earns anything for the organizations paying to store it. All of it carries breach risk, storage cost, and mounting legal exposure as retention laws tighten worldwide. The new patent’s purpose: a governed path, either lawfully deleted or safely used, without a human ever reading the underlying record.
THE FIRST LAYER: TRIAGE WITHOUT READING
Band-Based Archive Triage, short form BBAT — the system’s first move is to look at the label, never the letter.
The new invention’s triage layer examines only metadata — age, category, jurisdiction — never the stored content itself. Each record is normalized onto a 0-to-1 scale and compared against a governed threshold. A ten-year-old customer file might normalize to [0.71, 0.76] against a retention ceiling of [0.00, 0.70] — it fails the check and is flagged for lawful deletion, untouched by human eyes.
THE SECOND LAYER: DDME — DARK DATA MONETISATION ENGINE
What clears triage still cannot leave the vault in raw form.
For records cleared for use rather than deletion, the Dark Data Monetisation Engine derives a normalized signal inside a sealed execution environment, then
deletes the source material before anything transmits outward. A dormant compliance archive might derive a monetisation band of [0.58, 0.63] against an authorized transmission ceiling of [0.00, 0.65] — it clears, and only the derived band ever leaves the vault, never the underlying record.
THE THIRD LAYER: BDTS — BAND-DERIVED TRAINING SIGNAL
A separate signal, purpose-built for training rather than general use.
The Band-Derived Training Signal extends the same derivation logic specifically toward AI training data, producing a normalized, non-reversible signal bound by a cryptographic seal rather than a general-purpose output. A dormant archive cleared for training use might derive a BDTS band of [0.55, 0.60] against an authorized ceiling of [0.00, 0.65] — it clears, and the model learns only from the sealed, population-level signal.
THE FOURTH LAYER: WATCHING MANY RECORDS AT ONCE
Cross-Agent Aggregation and Deconfiiction, short form CAAD — no single record tells the whole story. A pattern across thousands might.
A fourth layer watches for patterns across large batches rather than single files — flagging, for instance, when many unrelated dormant records suddenly show the same unusual access pattern. A batch of 40,000 archived files might trip an aggregate indicator of [0.66, 0.70] against a systemic-risk ceiling of [0.00, 0.60] — the batch is held, and the pattern itself, not any one file, becomes the reviewed event.
THE FIFTH LAYER: A RECEIPT, NOT A PROMISE
The ACR Governance Layer — every decision leaves a sealed, checkable trace behind it.
Each governed outcome — deleted, derived, or held — produces a sealed receipt recording what was decided and under what authority, generated at the moment of the decision rather than reconstructed afterward. That receipt, not a corporate assurance, is what the filing offers an auditor, a regulator, or a buyer trying to verify what actually happened to a given record.
THE SIXTH LAYER: A FORWARD-LOOKING WATCHER
Systemic Pattern Analysis from Receipts, short form SPAR — a separate signal fiags risk before it compounds, without touching anything.
A predictive layer tracks a record’s or a batch’s trajectory over time, distinct from the triage decision itself — flagging drift toward risk before it fully materializes. It can only raise an advisory; it cannot alter a governing rule or a sealed token on its own authority. The decision stays with the governed process, not with the watcher.
WHY GLOBAL DATA, NOT JUST ONE INDUSTRY
The filing targets a universal liability, not a single sector’s problem.
Every industry holding old records — banking, healthcare, insurance, telecom, government archives — faces the identical dead-data liability: storage cost without return, and breach risk without benefit, regardless of what business the organization
is actually in. The filing’s proposition is sector-agnostic by design, tested on the shape of the data problem itself rather than the specific industry producing it.
WHY BILLIONAIRE ALLOCATORS SHOULD CARE
Dormant data is a balance-sheet liability most boards have never priced.
For sovereign funds, institutional investors, and hyperscale operators, unmonitored dormant storage is rarely modeled as risk — it typically sits as a sunk cost, unexamined. A governed triage layer changes that calculation: liability becomes either eliminated through lawful deletion or converted into a measured, receipted asset through governed derivation.
QUICK FAQS
Does this replace the original 0→1 Doctrine patent?
No. It extends the same governing principle into dormant, previously stored data — a new child filing under the same parent framework.
Does it prove superintelligence has arrived?
No. It remains neutral on that debate, testing one governed action at a time regardless of how the larger question resolves.
Does it read or expose the underlying stored records?
No. Triage operates on metadata only; any derived signal leaves the vault after the source record is deleted.
What can a live demonstration actually show?
Whether a specific proposed action clears or fails its governed boundary under real testing
— not a guarantee extending beyond what is tested.
CLOSING NOTE
Zettabytes of dormant data have sat as pure liability for decades. This filing proposes a governed path out — lawfully deleted, or safely used, never both left to guesswork.
Live: www.0to1doctrine.com
The inventor describes live API testing, governed against ungoverned, side by side.
THE INVENTOR
Vatsal Soin is a system theorist, serial inventor and entrepreneur whose work spans AI decision governance, biometric authorization, and — with this filing — dormant data governance globally. His domain-agnostic portfolio also reaches into apparel: an August 2026 grant introduced an AI-powered footwear system and the Global Sharable Size Card invention. His filings span six continents, with grants in the US, India, Japan, and South Africa. He is a SIM–RMIT and NTU alumnus.
SELECTED REFERENCES
Granted: US Patent 12,446,652 B2 · Japan Patent 7560909 · India Patents 454081 and 599317. Filed: PCT/IN2025/051943 · US 19/489,595 · India 202511115781 · Australia AU2022450649. India 202611113867 (23 September 2026).
DISCLAIMER
Informational only. Not certified. No endorsement implied. Not investment advice. Examples are illustrative, not field results. Vatsal Soin · © 2026 All Rights Reserved